I passed my 312-50v13 exam in the first attempt. Thanks to TorrentVCE for providing the latest dumps that are surely a part of the original exam.
 Hugo


Complete, current, and immediate — that is what TorrentVCE delivers for the 312-50v13 exam. Payment confirmation unlocks the full ECCouncil Certified Ethical Hacker Exam (CEH v13 AI) materials at once, with expert-verified answers and 365 days of free updates included.
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Information Security and Ethical Hacking Overview | 6% | - Information Security Overview
|
| Topic 2: Sniffing and Evasion | 10% | - Network Sniffing
|
| Topic 3: System Hacking | 17% | - System Hacking Tools and Countermeasures
|
| Topic 4: Malware Threats | 8% | - Malware Analysis and Distribution
|
| Topic 5: Wireless Network Attacks | 9% | - Wireless Network Concepts
|
| Topic 6: Cloud and Container Attacks | 10% | - Cloud Computing Concepts
|
| Topic 7: Web Application Attacks | 19% | - Hacking Web Servers and Web Applications
|
| Topic 8: Vulnerability Analysis | 7% | - Vulnerability Assessment Concepts
|
| Topic 9: Enumeration | 15% | - Enumeration Concepts
|
| Topic 10: Mobile Platform and IoT Attacks | 7% | - Mobile Platform Attack Vectors
|
| Topic 11: Reconnaissance Techniques | 21% | - Footprinting and Reconnaissance
|
| Topic 12: Cryptography and Post-Exploitation | 13% | - Post-Exploitation Techniques
|
The latest exam information lists 125 questions for the 312-50v13 exam, to be completed within 240 minutes minutes. Knowing the format cold is half the battle — timed practice handles the other half.
These are the core domains of the ECCouncil Certified Ethical Hacker Exam (CEH v13 AI) blueprint:
The remaining domains appear in the full official outline, all of which our bank addresses.
ECCouncil sets the following prerequisites for the ECCouncil Certified Ethical Hacker Exam (CEH v13 AI): Mandatory: 2 years of work experience in the domain OR completion of an EC-Council official training. For candidates without experience, an alternative is to take the CEH exam and submit an exam eligibility application with USD 100 fee..
Check the current requirements on the official certification page before scheduling.
Validity is maintained, not assumed. Our dedicated IT team checks the system and pushes new versions to the site continuously, so the 312-50v13 bank on sale is always the latest — with expert-verified answers across the ECCouncil Certified Ethical Hacker Exam (CEH v13 AI) objectives. You can also pick the format that fits your devices: an easy-to-read PDF, a Windows PC test engine, or a browser-based online engine for Windows, Mac, Android, and iOS. Questions? Support replies to instant messages and emails within two hours.
Upon successful payment, the complete materials are available immediately: a download link on screen and an automatic email to your mailbox within about a minute. If nothing arrives within two hours, check spam and contact support. Every purchase carries a 365-day service warranty — you can download the latest valid version free whenever it is released, no matter when you bought — and a 50% renewal discount follows when the period ends.
Yes, we keep our promises — in writing. If you fail the corresponding exam within 60 days of purchase, email us a scanned copy of your enrollment slip and your official Score Report PDF within two days of the exam date; we process verified refunds in full within seven days. The exclusions are plain: exams taken within three days of purchase, candidate names that do not match the payer, and free or expired products. If you prefer, we will exchange your product for two others of equal value at no charge.
As of the latest information, the 312-50v13 exam's passing score is 70% and the registration fee is USD 1,199. ECCouncil can adjust either figure, so verify both on the official site before you book.
Which patch management strategy is most effective?
Correct Answer: D 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
A penetration testing team was engaged by a manufacturing company in Detroit to perform an internal security assessment of its production control systems. During the engagement, the team identified unauthorized remote access tools operating within the network, along with the transfer of proprietary manufacturing blueprints to an external account.
Analysis of system activity showed that the actions were carried out using valid user credentials associated with privileged system access.
What classification of attack best describes this incident?
Correct Answer: D 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
Which of the following addresses the secrecy and privacy of information?
Correct Answer: A 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
At Bayview University in San Francisco, California, ethical hacker Sofia Patel is evaluating security controls on Android 11 tablets used by staff. To simulate an attack, she installs KingoRoot.apk directly on one of the devices. The application leverages system vulnerabilities to elevate privileges without requiring a computer connection. Based on the module, which feature of this rooting approach makes the attack effective?
Correct Answer: D 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
During a red team assessment at Sunshine Credit Union in Miami, ethical hacker Laura demonstrates a weakness in the company ' s session handling process. She shows that once a user logs in, the same authentication token assigned before login continues to be valid without being refreshed. Laura explains that an attacker could exploit this flaw by tricking a victim into authenticating with a value already known to the attacker, gaining access afterward. To mitigate this risk, the IT team agrees to apply a countermeasure focused on proper session lifecycle management.
Which countermeasure should the IT team implement?
Correct Answer: A 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
Viewing page 1 out of 185 pages.
Viewing questions 1-5 out of 925 questions.
Over 89730+ Satisfied Customers
I passed my 312-50v13 exam in the first attempt. Thanks to TorrentVCE for providing the latest dumps that are surely a part of the original exam.
Hugo
The delivery date is as quick as a flash, i am in a hurry to take 312-50v13 exam and many thanks!
 Murray

Today, I have just received my congratulations letter that I passed my 312-50v13 exam.
 Herman

I am the only one of my colleagues who pass the exam. So proud. Thnaks to 312-50v13 dumps.
 Rodney
I am your old customers and recently just passed my 312-50v13 exam.
 Hubery
I wrote 312-50v13 exam today and remembered every question of 312-50v13 dump. I found 90% questions of real exam was what I wrote. Very valid dump!
 Jerry
TorrentVCE have made my work easier, 312-50v13 exam is not tough anymore. Thanks!!!
 Edison
I want to suggest you to all of you for the sake of your 312-50v13 exam, because they are outstanding.
 Jonas
Just passed my 312-50v13 exam! Thanks for the 312-50v13 exam dumps, they helped me a lot!
 Ira
It is one of the best 312-50v13 preparation dump I've ever used. I just passed the 312-50v13 test! Thanks to the 312-50v13 simulator, I was ready even for the most challenging questions.
 Tiffany
I cant believe that I passed the 312-50v13 test with a high score.
 Lawrence
Passed 312-50v13 exam today with 90%. I suggest you guys should study well with this dumb and the training materials what you have. And you will pass without problem.
 Una
The concrete knowledge was really interesting and kept me fresh through out the 312-50v13 preparations. I have already recommended your products to my friends and I will recommend where ever I will get a chance. Thanks!
 Lambert
I had failed the exam with questions from other site but studied with the 312-50v13 practice guide here and appeared again to pass the exam. Thank you for all your support! You are the best.
 Victoria
This 312-50v13 practice tests is enough. I passed exam when i use it. Good! I will use your dumps to pass my next exam as well.
 Marico
I will introduce this TorrentVCE to my friends if they have exams to attend, because i pass my 312-50v13 with its dumps!
 Ida
TorrentVCE Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
If you prepare for the exams using our TorrentVCE testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
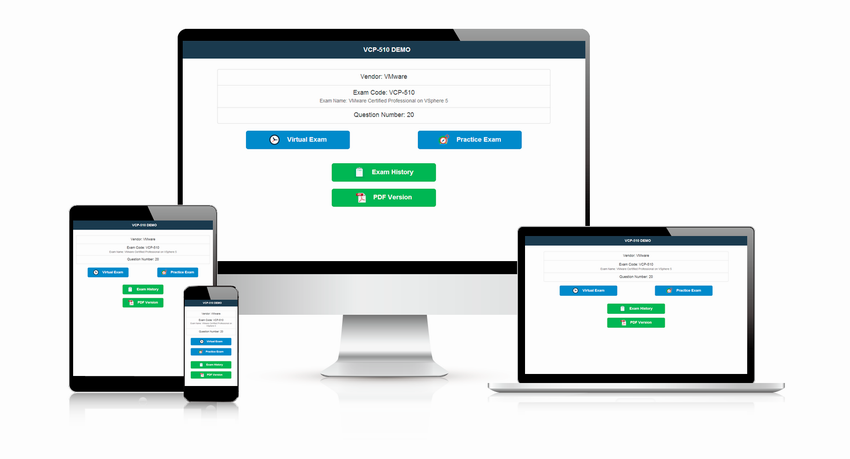
TorrentVCE offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
To help our candidate solve the difficulty in Real Exam, we prepared the Most Reliable Valid Study Torrent for the Exam Preparation. Our aim is help our candidates realize their ability by practicing our Updated Practice Torrent.
